<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="3.10.0">Jekyll</generator><link href="/feed.xml" rel="self" type="application/atom+xml" /><link href="/" rel="alternate" type="text/html" /><updated>2026-05-03T20:52:57+00:00</updated><id>/feed.xml</id><title type="html">rubysecurity.org</title><subtitle>Cloud Architect / DevOps Engineer / SRE / Developer | /root</subtitle><author><name>Alpha01</name></author><entry><title type="html">AI Revolution</title><link href="/ai/ai-revolution" rel="alternate" type="text/html" title="AI Revolution" /><published>2026-05-03T00:00:00+00:00</published><updated>2026-05-03T00:00:00+00:00</updated><id>/ai/ai-revolution</id><content type="html" xml:base="/ai/ai-revolution"><![CDATA[<p>As always, I’m late to the party when it comes to latest and greatest new things. In this case it’s AI (sort of). Not as a consumer by any means, as I use AI extensively on a daily basis for quite some time now. My lateness has been to the actual AI technology ecosystem front. Terms and concepts like LLM, Agents, MCP, etc. just a year ago were completely new to me. So it’s been amazing to see just how incredibly fast the tech world has become and leaning towards too. The AI Revolution is here and here to stay.</p>

<p>Being in the technology field for almost 20 years now. I feel software development and automation are at the forefront of this amazing time in tech. As such much of my focus is and will be on how to adapt AI into my processes. This probably also means a lot of cool new content coming to my little corner of the internet!</p>]]></content><author><name>Alpha01</name></author><category term="ai" /><category term="ai" /><summary type="html"><![CDATA[As always, I’m late to the party when it comes to latest and greatest new things. In this case it’s AI (sort of). Not as a consumer by any means, as I use AI extensively on a daily basis for quite some time now. My lateness has been to the actual AI technology ecosystem front. Terms and concepts like LLM, Agents, MCP, etc. just a year ago were completely new to me. So it’s been amazing to see just how incredibly fast the tech world has become and leaning towards too. The AI Revolution is here and here to stay.]]></summary></entry><entry><title type="html">Kubestronaut Journey Part 4: Kubernetes and Cloud Native Security Associate (KCSA)</title><link href="/kubernetes/kubestronaut/kcsa" rel="alternate" type="text/html" title="Kubestronaut Journey Part 4: Kubernetes and Cloud Native Security Associate (KCSA)" /><published>2025-08-09T00:00:00+00:00</published><updated>2025-08-09T00:00:00+00:00</updated><id>/kubernetes/kubestronaut/kcsa</id><content type="html" xml:base="/kubernetes/kubestronaut/kcsa"><![CDATA[<p><a href="https://www.credly.com/badges/241f5b77-aca6-498c-84f4-e0d239e954dd" target="_blank"><img src="/assets/kubernetes/kcsa_badge-new.png" alt="KCSA Badge" width="300" height="300" /></a></p>

<p>The  <a href="https://training.linuxfoundation.org/certification/kubernetes-and-cloud-native-security-associate-kcsa/" target="_blank">Kubernetes and Cloud Native Security Associate (KCSA)</a> exam is a an interesting one. Much like the other associate level exam, <a href="https://www.rubysecurity.org/kubernetes/kubestronaut/kcna" target="_blank">Kubernetes and Cloud Native Associate (KCNA)</a>, this is a traditional question and answer exam. A lot of the object objectives on this exam are theory based, like Cloud security models, Security compliance frameworks, and general basic level of Pod/Container security related configuration in Kubernetes.</p>

<p>The major motivation for me on embarking on this <a href="https://www.cncf.io/training/kubestronaut/" target="_blank">Kubestronaut</a> journey has been to learn new things Kubernetes that I otherwise wouldn’t know about. Certainly on all exams thus far have been the case. On this exam in particular I just learned about Pod Security Standards (PSS) and Pod Security Admission (PSA), which were new to me even after working with Kubernetes on an almost daily bases the last five years! (I use Kubernetes Admission Controllers instead)</p>

<p>I’m almost at the finish line on achieving <a href="https://www.cncf.io/training/kubestronaut/" target="_blank">Kubestronaut</a>, now the final exam I need to pass is arguably the most difficult one. <a href="https://training.linuxfoundation.org/certification/certified-kubernetes-security-specialist/">Certified Kubernetes Security Specialist (CKS)</a></p>

<h3 id="difficult-level">Difficult Level</h3>

<p>This was an easy exam. However unlike the scenario exam exercises or other question and answer exams where I have somewhat of an idea of what the answer will be. I felt as if on the questions that I answered wrong, were completely guesses on my part. Although the exam is easy in my point of view, I can certainly see it a being tricky to others. There were a few questions that touch topics I have zero to no working knowledge about, like AppArmor and seccomp.</p>

<h3 id="study-resources">Study Resources</h3>

<ul>
  <li><a href="https://learn.kodekloud.com/courses/kubernetes-and-cloud-native-security-associate-kcsa">KodeKloud Kubernetes and Cloud Native Security Associate (KCSA)</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="kubestronaut" /><category term="kubernetes" /><category term="kubestronaut" /><summary type="html"><![CDATA[]]></summary></entry><entry><title type="html">Kubestronaut Journey Part 3: Certified Kubernetes Administrator (CKA)</title><link href="/kubernetes/kubestronaut/cka" rel="alternate" type="text/html" title="Kubestronaut Journey Part 3: Certified Kubernetes Administrator (CKA)" /><published>2025-07-24T00:00:00+00:00</published><updated>2025-07-24T00:00:00+00:00</updated><id>/kubernetes/kubestronaut/cka</id><content type="html" xml:base="/kubernetes/kubestronaut/cka"><![CDATA[<p><a href="https://www.credly.com/badges/8c44d61e-2f10-43d3-b404-f9de24dedf62" target="_blank"><img src="/assets/kubernetes/cka_badge.png" alt="CKA Badge" width="300" height="300" /></a></p>

<p>Quite a lot things happened between the six months of my <a href="https://www.rubysecurity.org/kubernetes/kubestronaut/ckad" target="_blank">CKAD renewal</a> and now the CKA that allowed me to finally take the exam.</p>

<p>Needless to say I was able to successfully renew my <a href="https://training.linuxfoundation.org/certification/certified-kubernetes-administrator-cka/" target="_blank">Certified Kubernetes Administrator (CKA)</a> certification for two more years and now I’m just two steps away from becoming a <a href="https://www.cncf.io/training/kubestronaut/" target="_blank">Kubestronaut</a>. The next exam that I’ll be doing will be the <a href="https://training.linuxfoundation.org/certification/kubernetes-and-cloud-native-security-associate-kcsa/" target="_blank">Kubernetes and Cloud Native Security Associate (KCSA)</a>.</p>

<h3 id="difficult-level">Difficult Level</h3>

<p>The only major difference between the version that I took over three ago from the one I just passed was that the current version had less question regarding etcd administration and Kubernetes upgrades (kubeadm approach). Aside from these two points, the questions were mostly very similar. Thus said, I did had to study new features like the <a href="https://gateway-api.sigs.k8s.io/" target="_blank">Kubernetes Gateway API</a>.</p>

<p>I don’t think anyone that took and passed the exam three years, would have a problem passing this exam now.</p>

<h3 id="study-resources">Study Resources</h3>

<ul>
  <li><a href="https://www.udemy.com/course/certified-kubernetes-administrator-with-practice-tests/">Certified Kubernetes Administrator (CKA) with Practice Tests</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="kubestronaut" /><category term="kubernetes" /><category term="kubestronaut" /><summary type="html"><![CDATA[]]></summary></entry><entry><title type="html">Certified Kubernetes Application Developer (CKAD) Study Guide, 2nd Edition</title><link href="/books/kubernetes/ckad-study-guide" rel="alternate" type="text/html" title="Certified Kubernetes Application Developer (CKAD) Study Guide, 2nd Edition" /><published>2025-01-11T00:00:00+00:00</published><updated>2025-01-11T00:00:00+00:00</updated><id>/books/kubernetes/ckad-study-guide</id><content type="html" xml:base="/books/kubernetes/ckad-study-guide"><![CDATA[<p>It’s been a while since I’ve read a technical book, and thankfully this is a good one!</p>

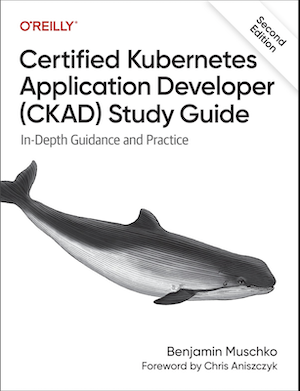
<p>I used this book as one of my study resources for the <a href="https://training.linuxfoundation.org/certification/certified-kubernetes-application-developer-ckad/" target="_blank">Certified Kubernetes Application Developer (CKAD)</a> certification exam that I recently took and passed (<a href="https://www.rubysecurity.org/kubernetes/kubestronaut/ckad" target="_blank">Kubestronaut Journey Part 2: Certified Kubernetes Application Developer (CKAD)</a>).</p>

<p>This book is outlined to follow the exam curriculum. In my opinion making it a perfect complimentary study resource. The chapters are relatively short, the examples cover the necessary topics without over flooding the user with information, but rather just provide enough information about the core concepts and what’s needed to pass the exam. Each chapter ends with lab exercise to do as way to fully validated the concepts covered in the chapter. An interesting thing about this book is that it has a companion <a href="https://www.oreilly.com/library/view/certified-kubernetes-application/0642572045296/" target="_blank">O’Reilly Video Course</a>, which I have access too using my work business account and used while reding this book. Thus said, this book can be used independently whether you have access to the companion video course.</p>

<h3 id="rating-35">Rating: 3/5</h3>

<p>Certified Kubernetes Application Developer (CKAD) Study Guide, 2nd Edition</p>

<p><a href="https://www.oreilly.com/library/view/certified-kubernetes-application/9781098152857/" target="_blank"><img src="/assets/books/ckad-study-guide.png" /></a></p>

<ul>
  <li>Chapter 1: Exam Details and Resources</li>
  <li>Chapter 2: Kubernetes in a Nutshell</li>
  <li>Chapter 3: Interacting with Kubernetes</li>
  <li>Chapter 4: Containers</li>
  <li>Chapter 5: Pods and Namespaces</li>
  <li>Chapter 6: Jobs and CronJobs</li>
  <li>Chapter 7: Volumes</li>
  <li>Chapter 8: Multi-Container Pods</li>
  <li>Chapter 9: Labels and Annotations</li>
  <li>Chapter 10: Deployments</li>
  <li>Chapter 11: Deployment Strategies</li>
  <li>Chapter 12: Helm</li>
  <li>Chapter 13: API Deprecations</li>
  <li>Chapter 14: Container Probes</li>
  <li>Chapter 15: Troubleshooting Pods and Containers</li>
  <li>Chapter 16: CustomResourceDefinitions (CRDs)</li>
  <li>Chapter 17: Authentication, Authorization, and Admission Control</li>
  <li>Chapter 18: Resource Requirements, Limits, and Quotas</li>
  <li>Chapter 19: ConfigMaps and Secrets</li>
  <li>Chapter 20. Security Contexts</li>
  <li>Chapter 21: Services</li>
  <li>Chapter 22: Ingresses</li>
  <li>Chapter 23: Network Policies</li>
</ul>]]></content><author><name>Alpha01</name></author><category term="books" /><category term="kubernetes" /><category term="kubernetes" /><category term="kubestronaut" /><summary type="html"><![CDATA[It’s been a while since I’ve read a technical book, and thankfully this is a good one!]]></summary></entry><entry><title type="html">Kubestronaut Journey Part 2: Certified Kubernetes Application Developer (CKAD)</title><link href="/kubernetes/kubestronaut/ckad" rel="alternate" type="text/html" title="Kubestronaut Journey Part 2: Certified Kubernetes Application Developer (CKAD)" /><published>2025-01-05T00:00:00+00:00</published><updated>2025-01-05T00:00:00+00:00</updated><id>/kubernetes/kubestronaut/ckad</id><content type="html" xml:base="/kubernetes/kubestronaut/ckad"><![CDATA[<p><a href="https://www.credly.com/badges/27b3233d-e6d8-4884-ae90-f7fd97b9f571" target="_blank"><img src="/assets/kubernetes/ckad_badge.png" alt="CKAD Badge" width="300" height="300" /></a></p>

<p>In my continuation of becoming a <a href="https://www.cncf.io/training/kubestronaut/" target="_blank">Kubestronaut</a>, I took the <a href="https://www.cncf.io/training/certification/ckad/" target="_blank">Certified Kubernetes Application Developer (CKAD)</a> exam. Unlike the <a href="https://www.rubysecurity.org/kubernetes/kubestronaut/kcna" target="_blank">Kubernetes and Cloud Native Associate (KCNA)</a> which is a question and answer exam, this exam is a hands on lab performance test (which personally I prefer). However this time around, their was one massive self-inflected gotcha that made this exam more difficult that it should’ve been. I opted to use my 13-inch 2021 M1 MacBook Pro for the exam. This made it extremely difficult to use the exam application due to the limited space of the remote workstation we have work in to do the respective exam assignments. Right from  the very start I became very agitated on the screen real estate that I had access too. I wasn’t able to easily switch between the Kubernetes documentation and the remote shell sessions. So I ended just using the built-in <code class="language-plaintext highlighter-rouge">kubectl explain</code> command line documentation for guidance. This worked well, except that I took way longer looking up information up to the point where I almost ran out of time and had to rush through the last 5 questions fearing that I wasn’t able going to finish the exam in time and fail due to not being able to answer the question! That’s about 1/3 of the entire exam!</p>

<h3 id="difficult-level">Difficult Level</h3>

<p>The questions ranged from really easy, to more mid-level and advanced (albeit simple) questions. The questions were straight forward. I practically used the same study material that I used when I first originally took the test on January 2022. Which was the <a href="https://www.udemy.com/course/certified-kubernetes-application-developer/">Udemy Kubernetes Certified Application Developer (CKAD) with Tests</a> course as well as the newly release <a href="https://www.oreilly.com/library/view/certified-kubernetes-application/0642572045296">O’Reilly Certified Kubernetes Application Developer (CKAD) Prep Course</a> and it’s companion book <a href="https://www.oreilly.com/library/view/certified-kubernetes-application/9781098152857/">Certified Kubernetes Application Developer (CKAD) Study Guide, 2nd Edition</a> for good measure.</p>

<p>Although I’m disappointed at myself on the final score, I was able to pass the exam with a score of 71/100. Not the score that I wanted, but given that I didn’t relied on using <a href="https://kubernetes.io/docs/home/" target="_blank">Kubernetes Documentation</a>, I’m content.  Next on my list will be completing (recertifying) the <a href="https://www.cncf.io/training/certification/cka/" target="_blank">Certified Kubernetes Administrator</a>.</p>

<p>Needless to say, for my next exam I’ll be connection my laptop to an external 27 display!</p>

<h3 id="study-resources">Study Resources</h3>

<ul>
  <li><a href="https://www.udemy.com/course/certified-kubernetes-application-developer/">Udemy Kubernetes Certified Application Developer (CKAD) with Tests</a></li>
  <li><a href="https://www.oreilly.com/library/view/certified-kubernetes-application/0642572045296">O’Reilly Certified Kubernetes Application Developer (CKAD) Prep Course</a></li>
  <li><a href="https://www.oreilly.com/library/view/certified-kubernetes-application/9781098152857/">Certified Kubernetes Application Developer (CKAD) Study Guide, 2nd Edition</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="kubestronaut" /><category term="kubernetes" /><category term="kubestronaut" /><summary type="html"><![CDATA[]]></summary></entry><entry><title type="html">Kubestronaut Journey Part 1: Kubernetes and Cloud Native Associate (KCNA)</title><link href="/kubernetes/kubestronaut/kcna" rel="alternate" type="text/html" title="Kubestronaut Journey Part 1: Kubernetes and Cloud Native Associate (KCNA)" /><published>2024-12-28T00:00:00+00:00</published><updated>2024-12-28T00:00:00+00:00</updated><id>/kubernetes/kubestronaut/kcna</id><content type="html" xml:base="/kubernetes/kubestronaut/kcna"><![CDATA[<p><a href="https://www.credly.com/badges/49bb3e7b-43d8-4dd1-8520-4b8d45537d47" target="_blank"><img src="/assets/kubernetes/kcna_badge.png" alt="KCNA Badge" width="300" height="300" /></a></p>

<p>It’s been almost three years since I’ve obtained the <a href="https://www.credly.com/badges/27b3233d-e6d8-4884-ae90-f7fd97b9f571" target="_blank">Certified Kubernetes Application Developer (CKAD)</a> and <a href="https://www.credly.com/badges/8c44d61e-2f10-43d3-b404-f9de24dedf62" target="_blank">Certified Kubernetes Administrator (CKA)</a> certifications. I was originally planning on recertifying these two Kubernetes certifications, however while at <a href="https://events.linuxfoundation.org/kubecon-cloudnativecon-north-america/" target="_blank">KubeCon</a> last month, I was excited to learn about the <a href="https://www.cncf.io/training/kubestronaut/" target="_blank">Kubestronaut Program</a>, which is a recognition to Kubernetes professionals that pass all five Kubernetes certifications. So I decided to accept the challenge and not only recertify my existing two certifications, but also take and pass the remaining three other certifications Kubernetes and Cloud Native Associate (KCNA), Cloud Native Security Associate (KCSA), and Certified Kubernetes Security Specialist (CKS) so I can become a “Kubestronaut”.</p>

<p>For my first exam on this journey, I’ve decided to start with the <a href="https://www.cncf.io/training/certification/kcna/" target="_blank">Kubernetes and Cloud Native Associate</a>, which is the easiest of them all. To prepare for the exam, I used the <a href="https://www.udemy.com/course/dive-into-cloud-native-containers-kubernetes-and-the-kcna/">Udemy Kubernetes Certified (KCNA) + Hands On Labs + Practice Exams</a> course (8 hours) and the <a href="https://www.oreilly.com/library/view/kubernetes-and-cloud/9780137993413/">O’Reilly Kubernetes and Cloud Native Associate (KCNA)</a> course (5 hours).</p>

<h3 id="difficult-level">Difficult Level</h3>

<p>Low, this was a very easy exam. I think anyone with moderate Kubernetes knowledge, can just use the <a href="https://www.udemy.com/course/dive-into-cloud-native-containers-kubernetes-and-the-kcna/">Udemy Kubernetes Certified (KCNA) + Hands On Labs + Practice Exams</a> course as their only study material can pass this exam. Thus said, this is also assuming that the candidate has also basic high-level knowledge of cloud and cloud native technologies. I’m pretty confident that I could’ve taken this exam without going through any of the mention study courses and I still would’ve easily passed it. However since this is meant to prepare myself for the more challenging exams, I’m still glad I study for this exam. I even learned new stuff along the way which is the main point of this entire journey!</p>

<p>I was able to successfully pass this exam with a score of 95/100. Next on my list will be completing (recertifying) the <a href="https://www.cncf.io/training/certification/ckad/" target="_blank">Certified Kubernetes Application Developer</a>.</p>

<h3 id="study-resources">Study Resources</h3>

<ul>
  <li><a href="https://www.udemy.com/course/dive-into-cloud-native-containers-kubernetes-and-the-kcna/">Udemy Kubernetes Certified (KCNA) + Hands On Labs + Practice Exams</a></li>
  <li><a href="https://www.oreilly.com/library/view/kubernetes-and-cloud/9780137993413/">O’Reilly Kubernetes and Cloud Native Associate (KCNA)</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="kubestronaut" /><category term="kubernetes" /><category term="kubestronaut" /><summary type="html"><![CDATA[]]></summary></entry><entry><title type="html">Simple Bash KVM Virtual Machine Startup and Shutdown Script</title><link href="/programming/bash/vm-shell-startup-script" rel="alternate" type="text/html" title="Simple Bash KVM Virtual Machine Startup and Shutdown Script" /><published>2024-12-14T00:00:00+00:00</published><updated>2024-12-14T00:00:00+00:00</updated><id>/programming/bash/vm-shell-startup-script</id><content type="html" xml:base="/programming/bash/vm-shell-startup-script"><![CDATA[<p>Given that I don’t want my <a href="https://www.rubysecurity.org/linux/ubuntu/running-ubuntu-server-on-an-intel-nuc-10th-i7">Intel NUC</a> homelab mini pc to sound like a jet engine all day. I wrote a simple bash script that would automatically startup and shutdown my kubernetes VMs easily each day. The script is cron friendly and it works like a charm.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Start VMs</span>
./rancher.sh start

<span class="c"># Stop (non-gracefully, use virsh shutdown instead)</span>
./rancher.sh destroy 
</code></pre></div></div>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c">#!/bin/bash</span>
<span class="c"># set -x</span>

<span class="nv">VMS</span><span class="o">=</span><span class="s2">"rancher rke2"</span>

<span class="nv">action</span><span class="o">=</span><span class="nv">$1</span>
<span class="k">if</span> <span class="o">[</span> <span class="nt">-z</span> <span class="nv">$action</span> <span class="o">]</span><span class="p">;</span> <span class="k">then
    </span><span class="nb">echo</span> <span class="s2">"No action passed"</span>
    <span class="nb">exit </span>1
<span class="k">elif</span> <span class="o">[[</span> <span class="s2">"</span><span class="nv">$action</span><span class="s2">"</span> <span class="o">!=</span> <span class="s2">"destroy"</span> <span class="o">&amp;&amp;</span> <span class="s2">"</span><span class="nv">$action</span><span class="s2">"</span> <span class="o">!=</span> <span class="s2">"start"</span> <span class="o">]]</span><span class="p">;</span> <span class="k">then
    </span><span class="nb">echo</span> <span class="s2">"Unsupported action: </span><span class="nv">$action</span><span class="s2">"</span>
    <span class="nb">exit </span>1
<span class="k">else
    </span><span class="nb">echo</span> <span class="s2">"Doing </span><span class="nv">$action</span><span class="s2">"</span>
<span class="k">fi

function </span>vm <span class="o">()</span> <span class="o">{</span>
    <span class="nv">vm</span><span class="o">=</span><span class="nv">$1</span>
    <span class="nv">current_vm_state</span><span class="o">=</span><span class="s2">""</span>
    <span class="nv">tmp</span><span class="o">=</span><span class="si">$(</span>virsh list <span class="nt">--all</span> | <span class="nb">grep</span> <span class="s2">" </span><span class="nv">$vm</span><span class="s2"> "</span> | <span class="nb">awk</span> <span class="s1">'{ print $3}'</span><span class="si">)</span>
    <span class="k">if</span> <span class="o">([</span> <span class="s2">"x</span><span class="nv">$tmp</span><span class="s2">"</span> <span class="o">==</span> <span class="s2">"x"</span> <span class="o">]</span> <span class="o">||</span> <span class="o">[</span> <span class="s2">"x</span><span class="nv">$tmp</span><span class="s2">"</span> <span class="o">!=</span> <span class="s2">"xrunning"</span> <span class="o">])</span>
    <span class="k">then
        </span><span class="nb">echo</span> <span class="s2">"</span><span class="nv">$vm</span><span class="s2"> does not exist or is shutdown!"</span>
        <span class="nv">current_vm_state</span><span class="o">=</span><span class="s2">"destroy"</span>
    <span class="k">else
       </span><span class="nb">echo</span> <span class="s2">"</span><span class="nv">$vm</span><span class="s2"> is running!"</span>
        <span class="nv">current_vm_state</span><span class="o">=</span><span class="s2">"start"</span>
    <span class="k">fi
    if</span> <span class="o">[</span> <span class="s2">"</span><span class="nv">$action</span><span class="s2">"</span> <span class="o">!=</span> <span class="s2">"</span><span class="nv">$current_vm_state</span><span class="s2">"</span> <span class="o">]</span><span class="p">;</span> <span class="k">then
        </span>virsh <span class="nv">$action</span> <span class="nv">$vm</span>
    <span class="k">fi</span>
<span class="o">}</span>

<span class="k">for </span>vm <span class="k">in</span> <span class="nv">$VMS</span><span class="p">;</span> <span class="k">do
    </span>vm <span class="s2">"</span><span class="nv">$vm</span><span class="s2">"</span>
<span class="k">done</span>
</code></pre></div></div>]]></content><author><name>Alpha01</name></author><category term="programming" /><category term="bash" /><category term="bash" /><category term="rancher" /><category term="kubernetes" /><summary type="html"><![CDATA[Given that I don’t want my Intel NUC homelab mini pc to sound like a jet engine all day. I wrote a simple bash script that would automatically startup and shutdown my kubernetes VMs easily each day. The script is cron friendly and it works like a charm. # Start VMs ./rancher.sh start # Stop (non-gracefully, use virsh shutdown instead) ./rancher.sh destroy #!/bin/bash # set -x VMS="rancher rke2" action=$1 if [ -z $action ]; then echo "No action passed" exit 1 elif [[ "$action" != "destroy" &amp;&amp; "$action" != "start" ]]; then echo "Unsupported action: $action" exit 1 else echo "Doing $action" fi function vm () { vm=$1 current_vm_state="" tmp=$(virsh list --all | grep " $vm " | awk '{ print $3}') if ([ "x$tmp" == "x" ] || [ "x$tmp" != "xrunning" ]) then echo "$vm does not exist or is shutdown!" current_vm_state="destroy" else echo "$vm is running!" current_vm_state="start" fi if [ "$action" != "$current_vm_state" ]; then virsh $action $vm fi } for vm in $VMS; do vm "$vm" done]]></summary></entry><entry><title type="html">Deploying Keycloak Identity Provider (IdP) for secure Rancher User Authentication Part 1</title><link href="/kubernetes/rancher/keycloak/keycloak-setup" rel="alternate" type="text/html" title="Deploying Keycloak Identity Provider (IdP) for secure Rancher User Authentication Part 1" /><published>2024-12-12T00:00:00+00:00</published><updated>2024-12-12T00:00:00+00:00</updated><id>/kubernetes/rancher/keycloak/keycloak-setup</id><content type="html" xml:base="/kubernetes/rancher/keycloak/keycloak-setup"><![CDATA[<p>No words can explain the constant headaches I’ve gotten throughout my career when working with LDAP in the Unix/Linux world. While I’ve had plenty of experience working with it in the past (<a href="https://www.rubysecurity.org/tag/ldap">https://www.rubysecurity.org/tag/ldap</a>), it’s certainly not the easiest or pleasant thing to work with. So I’m glad to see new (to me at least) Identity Provider (IdP) tools like <a href="https://www.keycloak.org/" target="_blank">Keycloak</a> that can help us manage user identities, authentication, and access control across applications and systems in a much easier fashion. But more importantly supporting integrations with authentication mechanisms like OpenID Connect (OIDC), OAuth2, SAML to name a few.</p>

<h3 id="environment-setup">Environment Setup</h3>

<p>To get up and running quickly, I opted to deploy Keycloak on a Ubuntu 24.04 VM instead of the container/kubernetes approach.</p>

<p>1). Install required packages.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>apt <span class="nb">install </span>openjdk-21-jre unzip
</code></pre></div></div>

<p>2). Download and extract keycloak.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">cd</span> /opt
wget https://github.com/keycloak/keycloak/releases/download/26.0.5/keycloak-26.0.5.zip
unzip keycloak-26.0.5.zip
<span class="nb">ln</span> <span class="nt">-s</span> keycloak-26.0.5 keycloak
</code></pre></div></div>

<p>3). Setup SSL certificates. At this stage, I had manually issued an Let’s Encrypt SSL certificate for <code class="language-plaintext highlighter-rouge">sso.rubyninja.org</code> for Keycloak. and copied it over to <code class="language-plaintext highlighter-rouge">/opt/keycloak/conf/certs</code></p>

<p>4). Update the following settings on <code class="language-plaintext highlighter-rouge">/opt/keycloak/conf/keycloak.conf</code>.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="c"># Hostname for the Keycloak server.</span>
<span class="nb">hostname</span><span class="o">=</span>sso.rubyninja.org

<span class="c"># The file path to a private key in PEM format.</span>
https-certificate-key-file<span class="o">=</span>/opt/keycloak/conf/certs/MYKEY.key

<span class="c"># The file path to a server certificate or certificate chain in PEM format.</span>
https-certificate-file<span class="o">=</span>/opt/keycloak/conf/certs/MYCERT.crt
</code></pre></div></div>

<p>5).  Create initial bootstrap admin username/password</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>/opt/keycloak/bin/kc.sh bootstrap-admin user
Enter username <span class="o">[</span>temp-admin]:temp-admin
Enter password:
Enter password again:
</code></pre></div></div>

<p>5). Start up the application</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>screen <span class="nt">-dm</span> /opt/keycloak/bin/kc.sh start <span class="nt">--verbose</span>
</code></pre></div></div>

<p>After login in with the temp-admin account, I had to manually create a separate admin user.</p>

<p>By no means this is a production ready setup, but for a homelab environment for testing, this setup is more than sufficient for me.</p>

<h3 id="resources">Resources</h3>

<ul>
  <li><a href="https://www.keycloak.org/getting-started/getting-started-zip">https://www.keycloak.org/getting-started/getting-started-zip</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="rancher" /><category term="keycloak" /><category term="kubernetes" /><category term="rancher" /><category term="keycloak" /><category term="security" /><summary type="html"><![CDATA[No words can explain the constant headaches I’ve gotten throughout my career when working with LDAP in the Unix/Linux world. While I’ve had plenty of experience working with it in the past (https://www.rubysecurity.org/tag/ldap), it’s certainly not the easiest or pleasant thing to work with. So I’m glad to see new (to me at least) Identity Provider (IdP) tools like Keycloak that can help us manage user identities, authentication, and access control across applications and systems in a much easier fashion. But more importantly supporting integrations with authentication mechanisms like OpenID Connect (OIDC), OAuth2, SAML to name a few.]]></summary></entry><entry><title type="html">Let’s Encrypt</title><link href="/awesome-applications/letsencrypt/lets-encrypt" rel="alternate" type="text/html" title="Let’s Encrypt" /><published>2024-12-10T00:00:00+00:00</published><updated>2024-12-10T00:00:00+00:00</updated><id>/awesome-applications/letsencrypt/lets-encrypt</id><content type="html" xml:base="/awesome-applications/letsencrypt/lets-encrypt"><![CDATA[<p>I’ve been using <a href="https://letsencrypt.org/getting-started/" target="_blank">Let’s Encrypt</a> for years, and it came to me that I’ve hardly ever really mentioned this awesome service at all! Let’s Encrypt is awesome, plain and simple. I use to throughout my homelab to setup and configure secure access.</p>

<p>Using this awesome is really straight forward. I use the <a href="https://github.com/acmesh-official/acme.sh" target="_blank">acme.sh</a> script for all ssh requests. The <a href="https://github.com/acmesh-official/acme.sh">acme.sh</a> script is simple and works beautifully.</p>

<h3 id="setup">Setup</h3>

<p>I use the <a href="https://github.com/acmesh-official/acme.sh?tab=readme-ov-file#2-or-install-from-git" target="_blank">git repository setup method</a>.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>git clone https://github.com/acmesh-official/acme.sh.git
<span class="nb">cd</span> ./acme.sh
./acme.sh <span class="nt">--install</span> <span class="nt">-m</span> my@example.com
</code></pre></div></div>

<p>The setup process will create a <code class="language-plaintext highlighter-rouge">~/.acme.sh</code> configuration environment that the script will use to save your Let’s Encrypt issued certificates in.</p>

<p>I use the <a href="https://github.com/acmesh-official/acme.sh?tab=readme-ov-file#8-automatic-dns-api-integration">Automatic DNS API integration</a> approach to verify and issue certificates. For this to work with Cloudflare, I simply just needed to create an <a href="https://developers.cloudflare.com/fundamentals/api/get-started/create-token/" target="_blank">API key</a> and export the following two variables.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="nb">export </span><span class="nv">CF_Key</span><span class="o">=</span><span class="s2">"EXAMPLEKEY"</span>
<span class="nb">export </span><span class="nv">CF_Email</span><span class="o">=</span><span class="s2">"my@example.com"</span>
</code></pre></div></div>

<p>Afterwards, it’s just a matter of using the <a href="https://github.com/acmesh-official/acme.sh" target="_blank">acme.sh</a> script.</p>

<p>For example:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>./acme.sh <span class="nt">--issue</span> <span class="nt">--dns</span> dns_cf <span class="nt">-d</span> rubyninja.org <span class="nt">-d</span> <span class="k">*</span>.antoniobaltazar.com <span class="nt">-d</span> <span class="k">*</span>.rubyninja.org <span class="nt">-d</span> <span class="k">*</span>.k8s.rubyninja.org <span class="nt">-d</span> <span class="k">*</span>.rubysecurity.org
</code></pre></div></div>

<p>The really cool thing is that the script is smart enough to save the environments under <code class="language-plaintext highlighter-rouge">~/.acme.sh/account.conf</code> for future use (certs are valid for 90 days). In addition it supports wildcards certificates, as well as it being cron friendly!</p>

<h3 id="resources">Resources</h3>

<ul>
  <li><a href="https://github.com/acmesh-official/acme.sh">https://github.com/acmesh-official/acme.sh</a></li>
  <li><a href="https://github.com/acmesh-official/acme.sh/wiki/dnsapi#dns_cf">https://github.com/acmesh-official/acme.sh/wiki/dnsapi#dns_cf</a></li>
  <li><a href="https://developers.cloudflare.com/fundamentals/api/get-started/create-token/">https://developers.cloudflare.com/fundamentals/api/get-started/create-token/</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="awesome-applications" /><category term="letsencrypt" /><category term="letsencrypt" /><category term="security" /><summary type="html"><![CDATA[I’ve been using Let’s Encrypt for years, and it came to me that I’ve hardly ever really mentioned this awesome service at all! Let’s Encrypt is awesome, plain and simple. I use to throughout my homelab to setup and configure secure access.]]></summary></entry><entry><title type="html">Deploying Rancher on my Homelab</title><link href="/kubernetes/rancher/rancher-setup" rel="alternate" type="text/html" title="Deploying Rancher on my Homelab" /><published>2024-12-07T00:00:00+00:00</published><updated>2024-12-07T00:00:00+00:00</updated><id>/kubernetes/rancher/rancher-setup</id><content type="html" xml:base="/kubernetes/rancher/rancher-setup"><![CDATA[<p>Finally! A new post on my technical site that I feel it’s post worthy. So, I’ve been working with Rancher on a daily basis for a few years now. The last time I ran this awesome application on my homelab, I was using <a href="https://rke.docs.rancher.com/">RKE</a> for the Kubernetes distribution. This time I’m using the new and improved <a href="https://docs.rke2.io/">RKE2</a>.</p>

<p>I wanted to have a Rancher environment on my homelab so I can experiment and play around with this awesome piece of technology. So I decided to spend some time setting up a fully functional Rancher environment on my homelab.</p>

<p>This is just the initial setup doc, of course I’m going to be adding more components to overly engineer my Rancher and Kubernetes homelab environment as much as possible.</p>

<h3 id="homelab-infra">Homelab Infra</h3>

<ul>
  <li>Ubuntu Host System (Intel NUC)</li>
  <li>Hypervisor: KVM</li>
  <li>Networking: BIND DNS and ISC DHCP</li>
</ul>

<h3 id="vm-host-information">VM Host Information</h3>

<ul>
  <li>OS: Ubuntu 24.04.x</li>
  <li>Hostname: https://rancher.k8s.rubyninja.org/</li>
  <li>Kubernetes Distribution: RKE2 v1.30.5+rke2r1</li>
</ul>

<h3 id="stack">Stack</h3>

<ul>
  <li>Rancher Community (Management Plane)</li>
  <li>MetalLB (LB IP Addressing)</li>
  <li>Nginx Ingress Controller (Ingress)</li>
  <li>Cert-manager ACME Let’s Encrypt Issuer (SSL/TLS)</li>
  <li>Istio (Service Mesh)</li>
  <li>Keycloak (Identity Provider)</li>
  <li>Knative (Serverles)</li>
  <li>Longhorn (Block Storage)</li>
  <li>Minio (Object Storage)</li>
  <li>Grafana Loki (Logs)</li>
</ul>

<p>0). Added the following Helm chart repositories:</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>helm repo add rancher-stable https://releases.rancher.com/server-charts/stable
helm repo add jetstack       https://charts.jetstack.io
helm repo add ingress-nginx  https://kubernetes.github.io/ingress-nginx
helm repo add metallb        https://metallb.github.io/metallb
helm repo update
</code></pre></div></div>

<p>1). Disabled rke2-ingress-nginx add-on <code class="language-plaintext highlighter-rouge">/etc/rancher/rke2/config.yaml</code></p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="na">disable</span><span class="pi">:</span> <span class="s">rke2-ingress-nginx</span>
</code></pre></div></div>

<p>2). Install RKE2</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>curl <span class="nt">-sfL</span> https://get.rke2.io | sh -
systemctl <span class="nb">enable </span>rke2-server.service

<span class="nb">export </span><span class="nv">PATH</span><span class="o">=</span><span class="nv">$PATH</span>:/var/lib/rancher/rke2/bin/
<span class="nb">export </span><span class="nv">KUBECONFIG</span><span class="o">=</span>/etc/rancher/rke2/rke2.yam
</code></pre></div></div>

<p>3). Install MetalLB</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>helm <span class="nb">install </span>metallb metallb/metallb <span class="nt">--version</span> 0.14.8 <span class="nt">--create-namespace</span> <span class="nt">-n</span> metallb-system
</code></pre></div></div>

<p>4). MetalLB Configuration for the Nginx Ingress Controller for Rancher</p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="s">kubectl -n metallb-system apply -f - &lt;&lt;EOF</span>
<span class="na">apiVersion</span><span class="pi">:</span> <span class="s">metallb.io/v1beta1</span>
<span class="na">kind</span><span class="pi">:</span> <span class="s">IPAddressPool</span>
<span class="na">metadata</span><span class="pi">:</span>
  <span class="na">name</span><span class="pi">:</span> <span class="s">rancher</span>
<span class="na">spec</span><span class="pi">:</span>
  <span class="na">addresses</span><span class="pi">:</span>
  <span class="pi">-</span> <span class="s">192.168.1.71-192.168.1.73</span>
<span class="nn">---</span>
<span class="na">apiVersion</span><span class="pi">:</span> <span class="s">metallb.io/v1beta1</span>
<span class="na">kind</span><span class="pi">:</span> <span class="s">L2Advertisement</span>
<span class="na">metadata</span><span class="pi">:</span>
  <span class="na">name</span><span class="pi">:</span> <span class="s">rancher</span>
<span class="na">spec</span><span class="pi">:</span>
  <span class="na">ipAddressPools</span><span class="pi">:</span>
  <span class="pi">-</span> <span class="s">rancher</span>
<span class="s">EOF</span>
</code></pre></div></div>

<p>5). Install Nginx Ingress Controller.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>helm <span class="nb">install </span>ingress-nginx ingress-nginx/ingress-nginx <span class="nt">--version</span> 4.11.3 <span class="nt">-n</span> ingress-system
</code></pre></div></div>

<p>6). Install cert-manager.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>helm upgrade <span class="se">\</span>
  cert-manager jetstack/cert-manager <span class="se">\</span>
  <span class="nt">--install</span> <span class="se">\</span>
  <span class="nt">--create-namespace</span> <span class="se">\</span>
  <span class="nt">--namespace</span> cert-manager <span class="se">\</span>
  <span class="nt">--version</span> v1.16.1 <span class="se">\</span>
  <span class="nt">--set</span> crds.enabled<span class="o">=</span><span class="nb">true</span> <span class="se">\</span>
  <span class="nt">--set</span> <span class="nv">dns01RecursiveNameservers</span><span class="o">=</span><span class="s2">"8.8.8.8:53"</span> <span class="se">\</span>
  <span class="nt">--set</span> <span class="nv">dns01RecursiveNameserversOnly</span><span class="o">=</span><span class="nb">true</span> <span class="se">\</span>
  <span class="nt">--set</span> global.logLevel<span class="o">=</span>4
</code></pre></div></div>

<p>I needed to use Google’s Public DNS for the recursive nameserver, otherwise it will default to my local BIND DNS which cert-manger owner verification process would fail because the requesting SSL/TLS certificates for <code class="language-plaintext highlighter-rouge">rancher.k8s.rubyninja.org</code> are hosted on local homelab BIND DNS server.</p>

<p>7). I’m using the DNS verification process for cert-manager Let’s Encrypt. So I needed to configure cert-manager to talk to Cloudflare since <code class="language-plaintext highlighter-rouge">rubyninja.org</code> public domain is hosted by them.</p>

<p>Create API key as outlined on the <a href="https://developers.cloudflare.com/fundamentals/api/get-started/create-token/">Cloudflare Create API token</a> document, and create the Kubernetes Secret with the corresponding API key data.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>kubectl create secret generic cloudflare-cred <span class="nt">--from-literal</span> api-key<span class="o">=</span><span class="s2">"&lt;retracted&gt;"</span> <span class="nt">-n</span> cert-manager
</code></pre></div></div>

<p>8). Now I was able to configure my <code class="language-plaintext highlighter-rouge">ClusterIssuer</code> cert-manager resource.</p>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="s">kubectl apply -f - &lt;&lt;EOF</span>
<span class="na">apiVersion</span><span class="pi">:</span> <span class="s">cert-manager.io/v1</span>
<span class="na">kind</span><span class="pi">:</span> <span class="s">ClusterIssuer</span>
<span class="na">metadata</span><span class="pi">:</span>
  <span class="na">name</span><span class="pi">:</span> <span class="s">letsencrypt-cloudflare-prod</span>
<span class="na">spec</span><span class="pi">:</span>
  <span class="na">acme</span><span class="pi">:</span>
    <span class="c1"># The ACME server URL</span>
    <span class="na">server</span><span class="pi">:</span> <span class="s">https://acme-v02.api.letsencrypt.org/directory</span>
    <span class="c1"># Email address used for ACME registration</span>
    <span class="na">email</span><span class="pi">:</span> <span class="s">&lt;RETRACTED&gt;</span>
    <span class="c1"># Name of a secret used to store the ACME account private key</span>
    <span class="na">privateKeySecretRef</span><span class="pi">:</span>
      <span class="na">name</span><span class="pi">:</span> <span class="s">letsencrypt-cloudflare-prod-key</span>
    <span class="na">solvers</span><span class="pi">:</span>
      <span class="pi">-</span> <span class="na">dns01</span><span class="pi">:</span>
          <span class="na">cloudflare</span><span class="pi">:</span>
            <span class="na">email</span><span class="pi">:</span> <span class="s">&lt;RETRACTED&gt;</span>
            <span class="na">apiKeySecretRef</span><span class="pi">:</span>
              <span class="na">name</span><span class="pi">:</span> <span class="s">cloudflare-cred</span>
              <span class="na">key</span><span class="pi">:</span> <span class="s">api-key</span>
        <span class="na">selector</span><span class="pi">:</span>
          <span class="na">dnsZones</span><span class="pi">:</span>
           <span class="pi">-</span> <span class="s2">"</span><span class="s">rubyninja.org"</span>
<span class="s">EOF</span>
</code></pre></div></div>

<p>9). Created the <code class="language-plaintext highlighter-rouge">cattle-namespace</code> namespace for the <code class="language-plaintext highlighter-rouge">Certificate</code> cert-manager object and SSL/TLS issued certificate that will be saved as a Kubernetes secret and later be used for the Rancher installation.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>kubectl create ns cattle-system
</code></pre></div></div>

<div class="language-yaml highlighter-rouge"><div class="highlight"><pre class="highlight"><code><span class="s">kubectl -n cattle-system apply -f - &lt;&lt;EOF</span>
<span class="na">apiVersion</span><span class="pi">:</span> <span class="s">cert-manager.io/v1</span>
<span class="na">kind</span><span class="pi">:</span> <span class="s">Certificate</span>
<span class="na">metadata</span><span class="pi">:</span>
  <span class="na">name</span><span class="pi">:</span> <span class="s">rancher-k8s-rubyninja-org</span>
<span class="na">spec</span><span class="pi">:</span>
  <span class="na">dnsNames</span><span class="pi">:</span>
  <span class="pi">-</span> <span class="s">rancher.k8s.rubyninja.org</span>
  <span class="na">issuerRef</span><span class="pi">:</span>
    <span class="na">group</span><span class="pi">:</span> <span class="s">cert-manager.io</span>
    <span class="na">kind</span><span class="pi">:</span> <span class="s">ClusterIssuer</span>
    <span class="na">name</span><span class="pi">:</span> <span class="s">letsencrypt-cloudflare-prod</span>
  <span class="na">secretName</span><span class="pi">:</span> <span class="s">rancher-k8s-rubyninja-org</span>
<span class="s">EOF</span>
</code></pre></div></div>

<p>Afterwards, the kubernetes.io/tls type Secret <code class="language-plaintext highlighter-rouge">rancher-k8s-rubyninja-org</code> was created on the cattle-system namespace with the corresponding certificate key pair issued by Let’s Encrypt. The <a href="https://cert-manager.io/docs/troubleshooting/">Cert-manager Troubleshooting</a> documentation has really straight forward explanation of the entire issuer process in case you run into problems getting an SSL/TLS certificate.</p>

<p>10). Finally, install Rancher.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>helm upgrade <span class="nt">--install</span> rancher rancher-stable/rancher <span class="nt">--version</span> 2.9.2 <span class="se">\</span>
  <span class="nt">--namespace</span> cattle-system <span class="se">\</span>
  <span class="nt">--set</span> <span class="nb">hostname</span><span class="o">=</span>rancher.k8s.rubyninja.org <span class="se">\</span>
  <span class="nt">--set</span> <span class="nv">agentTLSMode</span><span class="o">=</span><span class="s2">"system-store"</span> <span class="se">\</span>
  <span class="nt">--set</span> ingress.ingressClassName<span class="o">=</span>nginx <span class="se">\</span>
  <span class="nt">--set</span> ingress.tls.source<span class="o">=</span><span class="s2">"secret"</span> <span class="se">\</span>
  <span class="nt">--set</span> ingress.tls.secretName<span class="o">=</span><span class="s2">"rancher-k8s-rubyninja-org"</span> <span class="se">\</span>
  <span class="nt">--set</span> <span class="nv">bootstrapPassword</span><span class="o">=</span><span class="s2">"ChangeMe12345"</span>
</code></pre></div></div>

<p><strong>NOTE:</strong> For some reason the default bootstrap password didn’t seem to work for me, so I had to manually reset it at the Pod level.</p>

<div class="language-bash highlighter-rouge"><div class="highlight"><pre class="highlight"><code>kubectl <span class="nt">--kubeconfig</span> <span class="nv">$KUBECONFIG</span> <span class="nt">-n</span> cattle-system <span class="nb">exec</span> <span class="si">$(</span>kubectl <span class="nt">--kubeconfig</span> <span class="nv">$KUBECONFIG</span> <span class="nt">-n</span> cattle-system get pods <span class="nt">-l</span> <span class="nv">app</span><span class="o">=</span>rancher | <span class="nb">grep</span> <span class="s1">'1/1'</span> | <span class="nb">head</span> <span class="nt">-1</span> | <span class="nb">awk</span> <span class="s1">'{ print $1 }'</span><span class="si">)</span> <span class="nt">--</span> reset-password
</code></pre></div></div>

<h3 id="resources">Resources</h3>

<ul>
  <li><a href="https://developers.cloudflare.com/fundamentals/api/get-started/create-token/">https://developers.cloudflare.com/fundamentals/api/get-started/create-token/</a></li>
  <li><a href="https://cert-manager.io/docs/configuration/acme/dns01/#setting-nameservers-for-dns01-self-check">https://cert-manager.io/docs/configuration/acme/dns01/#setting-nameservers-for-dns01-self-check</a></li>
  <li><a href="https://cert-manager.io/docs/configuration/acme/dns01/cloudflare/">https://cert-manager.io/docs/configuration/acme/dns01/cloudflare/</a></li>
  <li><a href="https://cert-manager.io/docs/troubleshooting/">https://cert-manager.io/docs/troubleshooting/</a></li>
  <li><a href="https://medium.com/nerd-for-tech/ensure-having-a-rancher-admin-4ee62cd066e1">https://medium.com/nerd-for-tech/ensure-having-a-rancher-admin-4ee62cd066e1</a></li>
</ul>]]></content><author><name>Alpha01</name></author><category term="kubernetes" /><category term="rancher" /><category term="kubernetes" /><category term="rancher" /><category term="cert-manager" /><category term="letsencrypt" /><summary type="html"><![CDATA[Finally! A new post on my technical site that I feel it’s post worthy. So, I’ve been working with Rancher on a daily basis for a few years now. The last time I ran this awesome application on my homelab, I was using RKE for the Kubernetes distribution. This time I’m using the new and improved RKE2.]]></summary></entry></feed>